
(You can see some mixed English and Vietnamese :D, please feel free to use Google Translate extension if you’re interested in reading my notes)

Lambda:
🔑 Tips and tricks:
Lambda Insights ≠ X-Ray → phải thêm Insights extension layer
Luôn cần CloudWatchLambdaInsightsExecutionRolePolicy để Lambda ghi được logs/metrics
Tạo lambda functions để mà write data vào S3. Dev configure all functions to send logs and metrics to CloudWatch + receive reports from one Lambda
🔑 Lambda → private resources: cấu hình VPC access (private subnet + SG)
- Nếu muốn Lambda có IP thì phải đưa vào VPC
🔑 NAT/PrivateLink/VPN chỉ áp dụng khi có dịch vụ ngoài VPC or cross-account
🔑 Lỗi “timed out after X seconds” → kiểm tra và tăng function timeout; nếu xử lý I/O lớn, cân nhắc tăng bộ nhớ để có băng thông mạng/CPU cao hơn.
🔑 Cold start: chỉnh provisioned concurrency for Lambda function ($ option)
🔑 Dead-letter queue: cover cả TH Lambda chưa xử lí được (timeout)
🔑 Lambda call 3rd party service:
- Reserved concurrency limit số concurrent executions của Lambda function
🔑 Lambda có giới hạn:
.zip deployment package tối đa 250 MB uncompressed
50 MB compressed direct upload
250 MB compressed qua S3
Với dependency 500 MB vượt quá limit của .zip.
Giải pháp: dùng container image (max 10 GB).
Push image lên Amazon ECR, sau đó deploy Lambda từ container image
Lambda có thể access ECR images từ nhiều account khác nhau với permission
🔑 Lambda không hỗ trợ attach EBS volume → EBS chỉ gắn được cho EC2 → /tmp chỉ là ephemeral storage và reset mỗi lần cold start
🔑 Tips and tricks:
Lambda cần shared, persistent storage trong VPC → EFS + Access Point
Cần tách team cập nhật nội dung (lib/data) khỏi triển khai Lambda → đặt nội dung trên EFS, Lambda chỉ read (hoặc RW) qua Access Point
🔑 Lambda cần config dynamic → Dùng AppConfig Lambda extension (env var chỉ phù hợp thông số nhỏ, ít đổi → redeploy)
RDS:
🔑 Surge traffic: traffic tăng ko kiểm soát được → RDS Prox
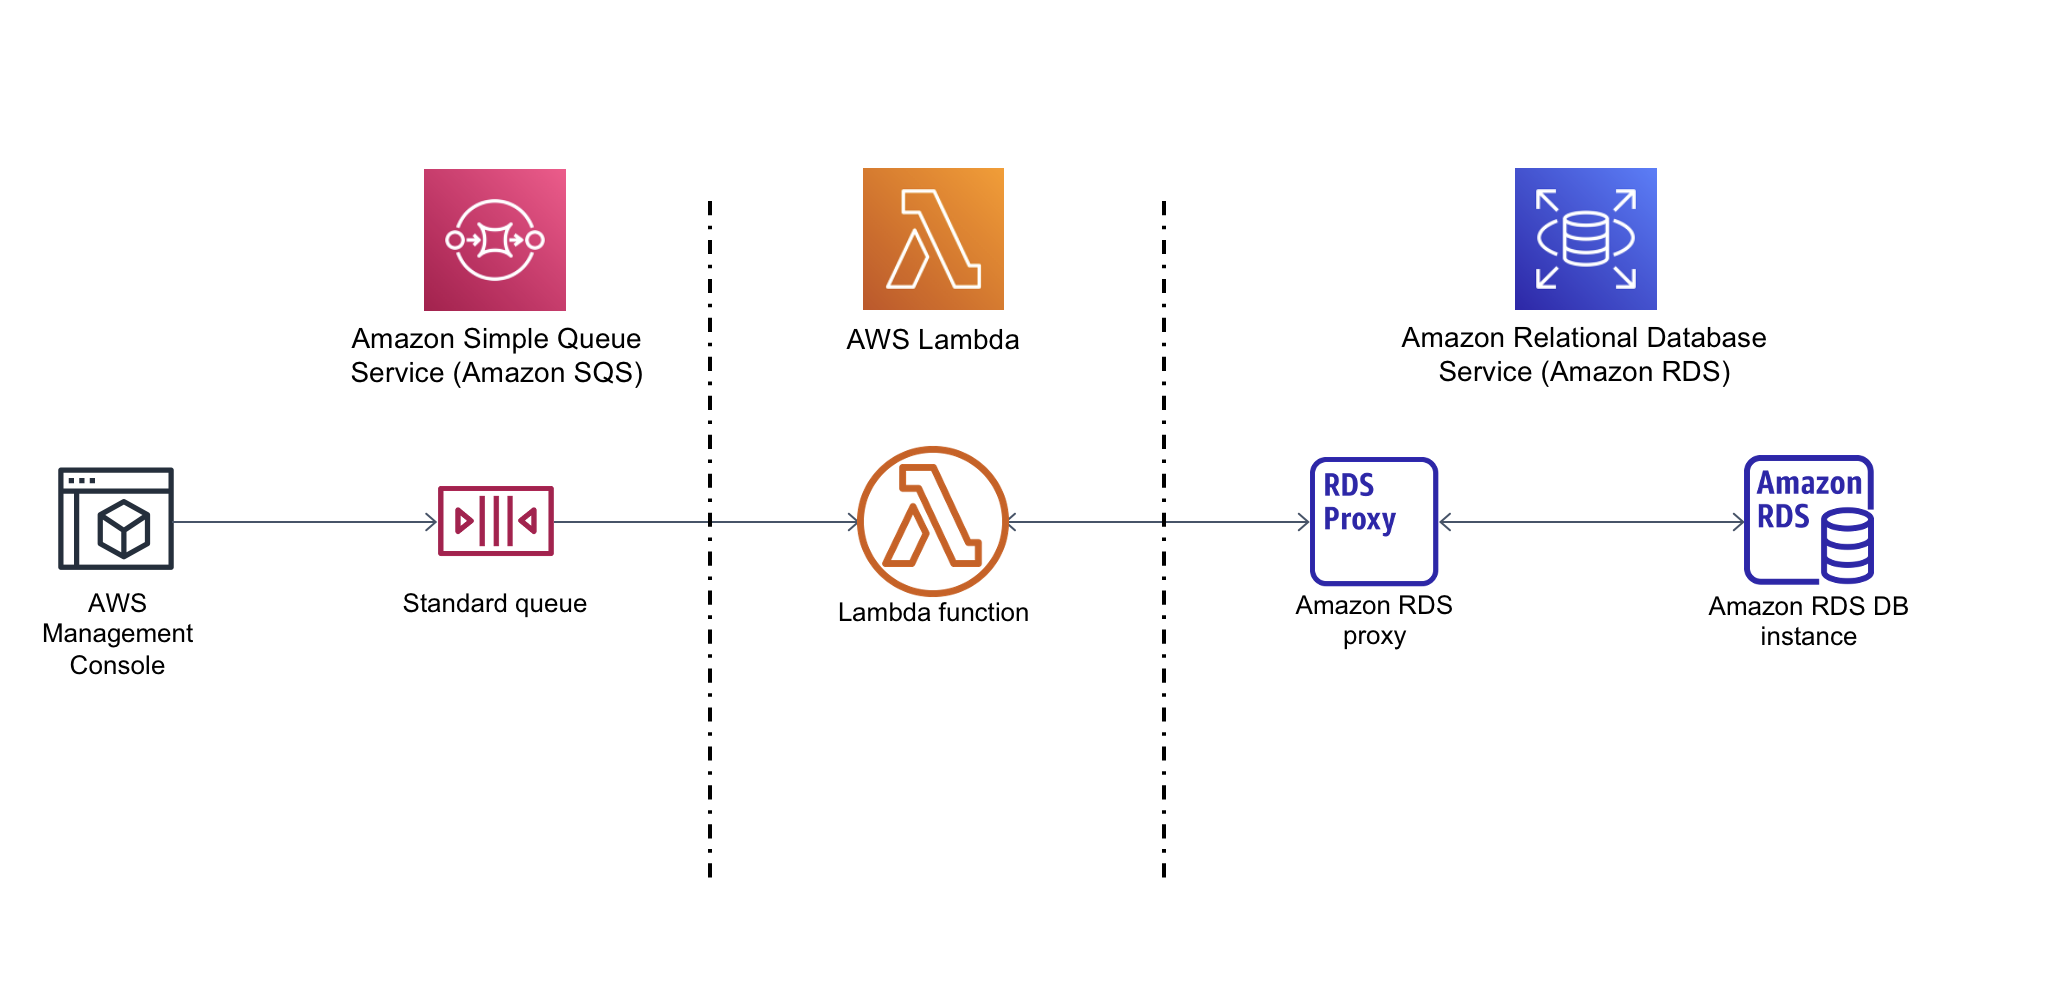
Lambda functions + connect to RDS db:
Requirement: Store DB creds securely
Secret manager:có cơ chế rotation by defaultMuốn auto-update secret → Secrets Manager + fetch runtime (ko dùng env vars)
System Manager chỉ lưu biến môi trườngchứ không phải lưu secrets (ko có cơ chế tự động rotation→ nếu cần phải liên kết vơiEvent Bridge (cron job + lambda)Không nên kết hợp Step Functions bởi vì add cost so với Event Bridge
Over-complicated cho simple scheduling task
Event Bridge đơn giản và rẻ hơn
Case: upload ảnh để tạo thumb upload vào bucket khác → đang 2 phút muốn xuống thành 30s → increase the amount of memory của Lambda
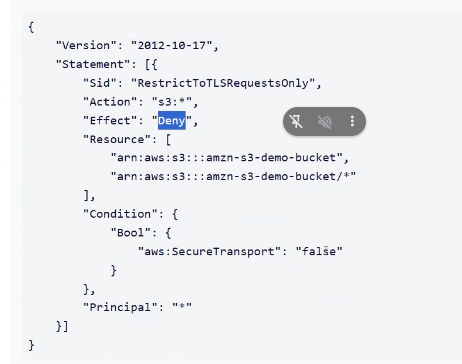
- Chỉnh cái bucket policy của S3 nếu mà muốn encrypt in transit:
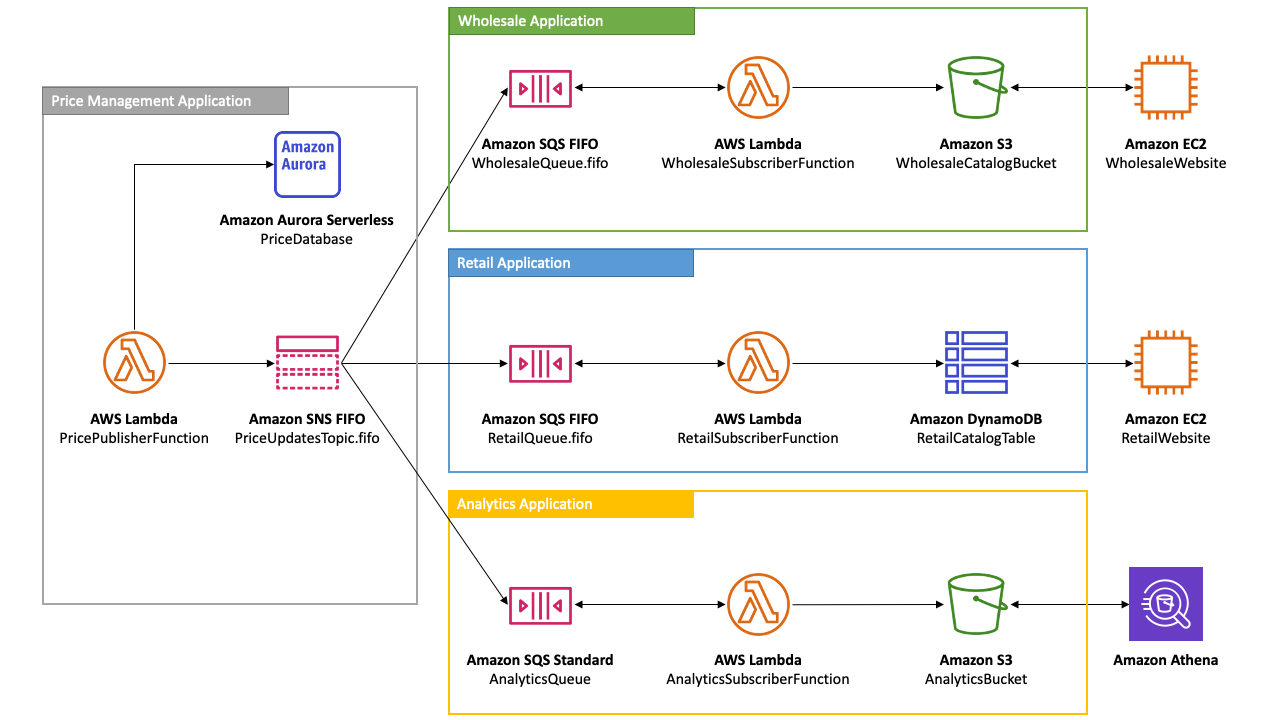
Lambda + SNS
Push process data to a subset (4 con consumer lambda functions) + Data phải được route dựa trên 1 field của data
Nếu gửi tới 4 con Filtering:SNS Topic (Filter gửi đến trường dữ liệu)💡Ko cần phải subcribe thằng data-processing đẩy vào topicLambda đang xử lí log:timestamp, processing time, and status of the requestsDùng SNS subscription filter policiesđể lọc thuộc tính → ko cần code routing hay quản lí nhiều topic/queue → overhead thấp nhấtAsync Lambda failures + retry → Dead-letter queue (DLQ)
DLQ option: SQS queue hoặc SNS topic →
Không support SQS queue FIFODLQ as event source = automatic retry mechanism
LEAST overhead → dùng native Lambda features (DLQ)
API Gateway + Lambda:
🔑 Tips and tricks:
3rd party auth + API Gateway = Lambda Authorizer!
🔑 Lambda function invoke REST API cho API Gateway. Hiện tại Request được invoke bởi consumer data-set trả bởi Lambda function thì visible
Chỉnh sửa lại req/res dưới dạng Template
Format lại data
Ko cần chỉnh sửa code Lambda
🔑 Tips and tricks:
Data formatting/transformation ở API Gateway = Mapping Templates!
Lambda + SQS:
🔑 Với Lambda + SQS, đặt Visibility Timeout → thời gian xử lý tối đa (thêm buffer) để tránh re-delivery.
X-Ray:
🔑 Tips and tricks:
Dùng AWS X-Ray để trace chi tiết latency giữa service → service
CloudWatch Logs chỉ đo tổng thời gian Lambda chạy, không tách riêng call đến downstream services
CloudWatch Lambda Insights = monitoring performance của Lambda, không thay thế X-Ray
KMS:
🔑 Tips and tricks: Cross-account secret access = IAM policy (Secrets Manager) + KMS key policy (Decrypt + DescribeKey)
priviledge: thì không chọn *, nếu mà service ko liên quan đến dịch vụ được mention thì ko chọn
KMS keysko thể replicate giữa accountsAWS managed keysko cho phép chỉnh key policy → ko đc thêm cross account access.
🔑 Encryption in transit → Lambda encryption helpers với env variables
At rest vs In transit:
Parameter Store / Secrets Manager / S3 = at rest
Lambda encryption helpers = in transit
KMS key + Lambda → cần grant permission cho execution role
🔑 Tips and tricks:
"Full control over KMS keys" → Customer managed key (không phải AWS managed key)
"Part of Lambda configuration" → Lambda environment variables
KMS key types:
AWS managed key = AWS quản lý, no full control
Customer managed key = full control (policies, rotation, access)
"Visible only to authorized entities" → KMS key policy control access
Parameter Store/DynamoDB = external storage, không phải "Lambda configuration"
Beanstalk Deployment strategies:
🔑 Tips and tricks:
Canary = thử nghiệm tính năng với một nhóm nhỏ trước (apply with a small group)
Linear = rollout tăng dần theo % (increase by percentages)
All-at-once = deploy toàn bộ ngay lập tức (deploy everything all together)
In-place = update trực tiếp, không có traffic splitting (update directly, without splitting)
🔑 Tips and tricks:
Rolling = batch update, có downtime nhỏ.
Immutable = zero downtime, nhưng all-or-nothing.
Traffic-splitting = canary style, forward % traffic.
Dynamo DB:
🔑 Khi dùng GSI thì không cần dùng chung partition key, LSI thì được tạo ra ngay từ ban đầu ko thay đổi được → cần dùng chung partition key
LSI = same partition key, different sort key
- Local secondary index hỗ trợ cả strongly consistent và eventually consistent reads
GSI = completely different partition key and sort key
- GSI chỉ hỗ trợ eventually consistent reads
Do đó nếu có latest data keyword thì phải remove eventually consistent options
🔑 Tips and Tricks:
Query = chính xác theo key condition, tiết kiệm RCUs
GetItem/BatchGetItem = chỉ biết rõ partition keys
Scan = tránh dùng nếu có index phù hợp
🔑 "New access pattern with different keys" → GSI (Global Secondary Index)
🔑 Optimize query performance and limit partition overload → partition key (UUID random → có độ phân tán cao → customer có unique value (evenly distributed + precent partition overload)
Dùng name, date có thể bị hot partitions (common names)
High cardinality keys: UUID, email, customer ID
Low cardinality keys: date, name, status, country
Hot partition = nhiều data/requests tập trung vào vài partitions → performance issue
Cloud Front:
Users request thì có 20 fields. Mỗi application transaction contains sensitive data cần mã hóa. Chỉ có những phần của app cần khả năng để decrypt data
🔑 Liên kết CloudFront distribution với Lambda@Edge function + dùng RSA để store
CloudFront có thể dùng WebSocket
🔑 Mã hóa sensitive env tại edge thì dùng CloudFront Filed-Level Encryption (riêng cái này chỉ encrypt sensitive field in POST request)
🔑 Set the Origin Protocol Policy set to Match Viewer:
1/ Origin Protocol Policy = Match Viewer (connection from CloudFront to ALB)
2/ Nghĩa là viewer dùng HTTPS thì CloudFront sẽ dùng HTTPS đến origin
3/ Encrypt data giữa CloudFront and ALB
S3:
🔑 Server-side encryption with S3 managed key (SSE-S3) mặc định thôi ko cần phức tạp + KMS thì share được thêm cho bên khác nữa
🔑Loại bỏ thông tin nhạy cảm: PII → S3 Object Lambda (sử dụng lambda function để thay đổi object) (gọi đến lambda, s3 trả về thông tin nhưng phải thông qua lambda)
🔑 Optimize S3 bucket for high request rates:
Dùng object key names distributed across multiple prefixes:
Multiple prefixes phân tán requests across multiple partitions trong S3
S3 tự động scale performance theo số prefixes
3,500 PUT/COPY/POST/DELETE và 5,500 GET/HEAD requests per second per prefix
Nhiều prefixes = tăng tổng throughput
Authen → Cognito (App, Mobile)
🔑 User Pool dùng để login
🔑 Identity Pool dùng để give permissions
Step Functions:
🔑 Chạy tuần tự nhiều Lambda → Step Functions (orchestration, retry, timeout, quan sát dễ)
API Gateway:
Case: REST API calls Lambda function
🔑 Chỉ có một môi trường là: API stage + trỏ 2 phía → tạo stage mới → points to prod Lambda function alias
Usage Plans trong Amazon API Gateway cho phép:
Định nghĩa quota (hạn mức) và rate limit (số request/giây) cho API
Gắn API key cho mỗi client để theo dõi và kiểm soát
Tạo nhiều gói sản phẩm như Free Tier, Pro, Enterprise...
🔑 Tips and tricks: Khi muốn commercialize API (biến API thành sản phẩm) → dùng API Gateway Usage Plans + API Keys!
🔑 Nhiều API GW → Dev đang làm việc với API in dev env → thay đổi ko được hiển thị
→ Redeploy the API đến stage hiện tại or to a new stage
Sửa API Gateway mà ko thấy thay đổi → Quên deploy to Stage
🔑 Types of APIs được hỗ trợ bởi API Gateway thì là right fit:
WebSocket APIs:
→ Lựa chọn tốt nhất cho real-time communication
- Kết nối hai chiều giữa client and server
Mô phỏng response API mà ko gọi đến backend thực tế
Test nhanh
🔑 Tips and tricks: Cần ẩn secret (API key) khỏi client → đặt ở API Gateway integration.
🔑 Tips and tricks:
WebSocket + Lambda authorizer → REQUEST authorizer + TTL cache.
Dùng $context.authorizer.* trong mapping template để truyền claims/roles mà không cần token mỗi request.
Container (ECS):
Elasticache:
🔑 Microsecond - Memcached support (multi-thread)
🔑 Redis (80% TH phải chọn)
WAF:
🔑 Chỉ filter requests ko mã hóa dữ liệu
SSL + ACM
Case: Áp dụng TTL coi certificate hết hạn khi nào
- Implement a solution to notify sec 90 days trước khi expires
🔑 Dùng AWS Config -> acm-certificate-expiration-check managed rule để chạy mỗi 24 tiếng. Tạo Event Bridge rile để includes event pattern mà specifies Config Rules Compliance Change → kết hợp bắn sự kiện noncompliant tới SNS topic (email team security)
SNS: FIFO topic
🔑 Yêu cầu: đúng thứ tự giao dịch của user
🔑 Configure the app SDK to publish notifications to SNS topic to send SMS messages to users
🔑 Không gửi trùng lặp (exactly-once delivery)
SNS Fan Out
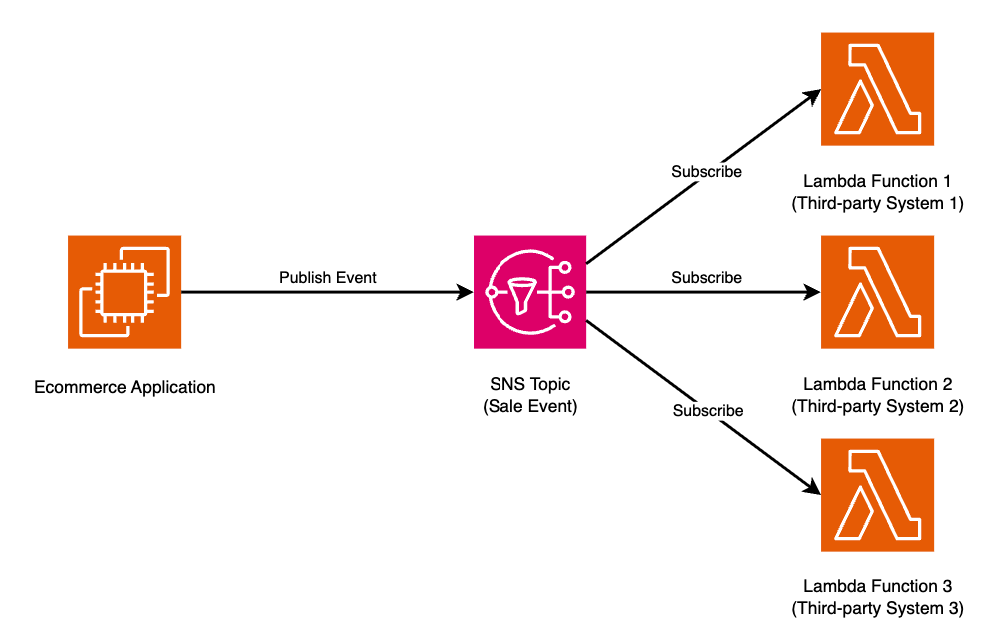
Gửi message đến tất cả subcribers → đồng thời mỗi lambda function là independent subcriber
Concurrent execution (nếu một lambda fail thì ko ảnh hưởng đến execution của 2 lambda còn lại)
SQS Queue:
🔑 One to one model → mỗi message chỉ được consume bởi một consumer (ko thể 3 lambda cùng process một message)
🔑 Message batching: lấy được nhiều message nhất
🔑 Long polling to query the queue for new messages + Batch messaging
🔑 Step Functions tốt cho orchestration nhưng tạo dependencies giữa các steps
- ✅ Use
StartMessageMoveTask APIto move messages from the dead-letter queue to the original SQS queue.
🔥SendMessageBatch chỉ gửi message mới, muốn dùng phải nhận → tốn công code
🔥ChangeMessageVisibility chỉ thay đổi timeout hiển thị message trong cùng queue → ko di chuyển message giữa DLQ và source
🔥PurgeQueue xóa vĩnh viễn tất cả message trong queue → mất dữ liệu
SAM:
SAM cung cấp template chuẩn cho serverless và support test local (sam local) and call SAM CLI within the stage of CodePipeline để build/test/deploy, đáp ứng nhu cầu
🔑 Flow chuẩn của SAM: build → package (S3) → deploy.
1. Build the SAM template locally.
2. Package the SAM template onto Amazon S3.
3. Deploy the SAM template from Amazon S3.
🔑 SAM CLI key commands:
sam local invoke:test Lambda locallysam local generate-event= tạo sample eventssam local start-api= test API Gateway locally
EFS:
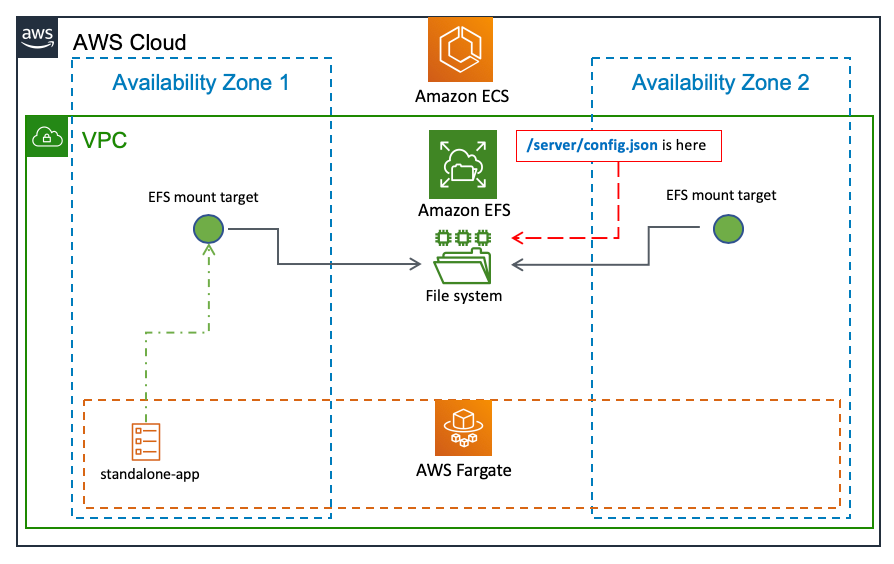
Đây là Network file system, hỗ trợ Fargate và nhiều tasks truy cập đồng thời, dữ liệu persist khi container dừng
CloudFormation:
🔑 CloudFormation xác định resouce dựa trên logical ID trong template, nếu đổi logical ID hoặc name, CloudFormation sẽ delete + tạo resource mới (nếu ko có Deletion Policy giữ lại)
🔑 CloudFormation template sẽ được deployed nhanh ở một region back-up (nếu mà sập) → Dùng StackSets
🔑 Nếu Dev viết Cloud Formation template (nếu có nhiều stack thì cần phải ImportValue function import từ stack Ref thì chỉ dùng cho cùng Stack)
Ngoài ra: Output với Export là bắt buộc để share values với other stacks, network team phải có output section
Mapping để define static lookup tables
Application Load Balancer:
Add X-Forwarded-For header to HTTP server log conf file
🔑 XFF header chứa original client IP address
Config:
🔑 support dynamic feature flags → application must poll on interval for new feature flag values → value sẽ được cached when they’re retrieved
🔑 AppConfig (Feature Flags) + AppConfig Agent hỗ trợ polling định kỳ, rollout/rollback an toàn, và local caching qua endpoint localhost → tối ưu công suất vận hành, chuẩn bị best practice cho feature flags.
IAM Identity Center (SSO):
🔑 IAM Identity Center credentials là temp cred có thời hạn (thường là 1-12 giở)
Dev cần re-authenticate (aws sso login) để refresh cred
Đây là behavior bth của SSO, ko phải lỗi conf
AWS Copilot:
🔑 Tips and tricks:
"AWS Copilot" + "automated deployment" → Copilot native pipeline feature
"MOST operationally efficient" → dùng native tools thay vì custom solutions
Copilot pipeline commands:
copilot pipeline init,copilot pipeline deploySAM = serverless, Copilot = containers
CDK (Cloud Development Kit)
❌ cdk synth
→ Chỉ generate CloudFormation template (YAML/JSON). Không tạo bucket bootstrap.
❌ cdk init
→ Dùng để khởi tạo 1 CDK project mới (app template), không liên quan tới deploy.
❌ cdk destroy
→ Xóa stack đã deploy. Không tạo bootstrap bucket và không khắc phục NoSuchBucket.
🔑 Tips and tricks:
Lần đầu deploy CDK vào account/region mới → luôn cần cdk bootstrap.
🧑💻 Code Deploy:
- Cần đăng ký instace (EC2/on-premises) và cấu hình đầy đủ (IAM/agent/tag
👨💻Code Artifact:
Code Artifact là package manager (npm, pip, maven ..) không phải công cụ test/debug local hay giả lập deployment
Native support cho .jar files và Java dependencies
Best practice cho managing application dependencies
🔑 ECR = container images, Code Artifact = packages/dependencies
🔑 Tips and tricks:
"Test/debug local" + "CodeDeploy package" → Nghĩ ngay đến CodeDeploy Local (codedeploy-local).
Cần unit/integration test trên cloud → nghĩ đến CodeBuild
Cần quản lý package/dependency → nghĩ đến CodeArtifact, không dùng để test deployment

🖥️ Monitoring services:
CloudWatch Logs:đều tích hợp native với API Gateway và Lambda- Nếu để filter by key words ví dụ “Error” trong log lines → Tạo metric filter as search term. Tạo alarm on this metric that notifies SNS topic khi metric is 1 or higher
CloudWatch Logs Insights:cho phép search, filter, và query log tập trung đa log group (Lambda + API Gateway)Logging ở API Gateway stage+ dùng Logs Insights là đường ngắn nhất để tìm lỗi end-to-endKo cần thêm service như Kinesis, Athena, or Open Search
Additional Notes:
🔑 IP addresses: X-Forwarded-For header: Check the original IP address from the request (suitable for Application Load Balancer tracing ..)


